Cloud Management & Migration
Strategic cloud migration planning and ongoing multi-cloud infrastructure management, ensuring performance, cost optimization, and security at every stage.
Learn moreOrange County, CA
Irvine's concentration of gaming studios, biotech firms, and financial technology companies creates a uniquely valuable target-rich environment for advanced persistent threat groups and organized cybercriminals. AdVran's SOC gives the continuous monitoring and expert threat hunting Irvine businesses need to defend intellectual property worth billions from adversaries willing to spend months inside a network before they make a move.
Frequently asked questions
Gaming source code is among the most targeted intellectual property globally. We set up monitoring around code repositories, build servers, and developer workstations that catches unauthorized access, bulk code downloads, and exfiltration via encrypted channels. Our detection rules are tuned for the development toolchains gaming studios actually use. Git, Perforce, Jenkins, and Unreal Engine build pipelines. So we catch threats that generic security tools miss entirely.
A supply chain attack compromises a trusted vendor or software component to get access to the real target. Irvine companies depend heavily on third-party libraries, SaaS platforms, and outsourced development. All potential entry points. Our SOC watches for indicators of supply chain compromise: unexpected software update behaviors, odd API calls from trusted applications, and vendor account use outside normal business patterns.
Yes. Our monitoring covers HIPAA, 21 CFR Part 11, and GxP requirements relevant to Irvine biotech firms. We keep audit trails for all security events, give tamper-evident logging, and produce compliance-ready reports that satisfy auditor requirements for continuous monitoring evidence.
What we offer
Strategic cloud migration planning and ongoing multi-cloud infrastructure management, ensuring performance, cost optimization, and security at every stage.
Learn more
Augment your in-house IT team with AdVran's certified engineers, 24/7 SOC, and compliance experts. Keep the people who know your business; add the depth you cannot hire.
Learn more
Continuous compliance monitoring, audit readiness, and risk management across HIPAA, CMMC, PCI-DSS, SOX, and other regulatory frameworks.
Learn more
Multi-layered cybersecurity for Southern California SMBs: EDR/MDR endpoint protection, email security, identity and access management, vulnerability management, SIEM monitoring, and security awareness training.
Learn more
Immutable backups, tested restore procedures, and disaster recovery as a service for California businesses. Built to actually work when ransomware hits, not just on paper.
Learn more
Responsive, security-aware help desk services covering device management, onboarding, offboarding, and day-to-day IT support for your entire workforce.
Learn more Rapid breach containment, forensic investigation, disaster recovery, and post-incident hardening to minimize damage and prevent recurrence.
Learn more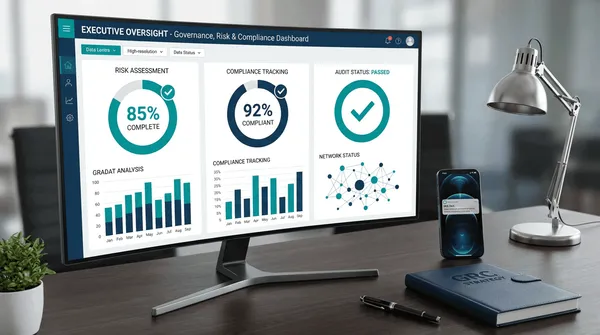
Fully managed IT services for Southern California SMBs. One flat monthly rate covers 24/7 monitoring, patch management, endpoint protection, and vCIO advisory - so your team stays focused on the business, not the infrastructure.
Learn more
End-to-end Microsoft 365 administration, security hardening, license optimization, and independent backup for California businesses. Built for SMBs and mid-market teams that outgrew the default settings.
Learn more
Design, deployment, and management of enterprise network infrastructure including SD-WAN, Wi-Fi, VPN, and multi-site connectivity.
Learn more
24/7 SOC monitoring, SIEM-powered threat detection, and proactive threat hunting to identify and neutralize attacks before they cause damage.
Learn more Targeted IT services covering email and spam protection, data backup and disaster recovery, and Microsoft 365 management for Southern California businesses with specific operational and compliance requirements.
Learn more