Cloud Management & Migration
Strategic cloud migration planning and ongoing multi-cloud infrastructure management, ensuring performance, cost optimization, and security at every stage.
Learn moreLos Angeles County, CA
Los Angeles sits at the crossroads of entertainment, media, and technology. Industries that attract some of the most sophisticated threat actors on the planet, from nation-state groups hunting unreleased content to ransomware gangs targeting post-production houses. AdVran's Security Operations Center gives continuous monitoring and proactive threat hunting built specifically for LA's high-stakes threat environment.
Frequently asked questions
LA entertainment firms face nation-state actors seeking unreleased content and scripts, ransomware groups that encrypt post-production workflows to extort studios, and insider threats from contractors with broad access to creative assets. Our SOC keeps detection rules tuned to these exact attack patterns, including monitoring for abnormal large file transfers, unauthorized access to digital asset management systems, and credential abuse across production environments.
Executive accounts are prime targets for business email compromise, SIM-swapping, and spear-phishing. We set up behavioral analytics around C-suite email, financial authorization workflows, and personal device activity. Our analytics baseline each executive's normal patterns and alert on anomalies. Like login attempts from unusual locations or bulk email forwarding rule changes. Before an attacker can use that compromised access.
Yes. Ransomware follows predictable pre-encryption behaviors: reconnaissance, privilege escalation, lateral movement, and shadow copy deletion. Our SIEM correlation rules and threat hunting playbooks target each of these stages. We've detected and contained ransomware during the lateral movement phase for multiple LA clients, stopping encryption entirely.
What we offer
Strategic cloud migration planning and ongoing multi-cloud infrastructure management, ensuring performance, cost optimization, and security at every stage.
Learn more
Augment your in-house IT team with AdVran's certified engineers, 24/7 SOC, and compliance experts. Keep the people who know your business; add the depth you cannot hire.
Learn more
Continuous compliance monitoring, audit readiness, and risk management across HIPAA, CMMC, PCI-DSS, SOX, and other regulatory frameworks.
Learn more
Multi-layered cybersecurity for Southern California SMBs: EDR/MDR endpoint protection, email security, identity and access management, vulnerability management, SIEM monitoring, and security awareness training.
Learn more
Immutable backups, tested restore procedures, and disaster recovery as a service for California businesses. Built to actually work when ransomware hits, not just on paper.
Learn more
Responsive, security-aware help desk services covering device management, onboarding, offboarding, and day-to-day IT support for your entire workforce.
Learn more Rapid breach containment, forensic investigation, disaster recovery, and post-incident hardening to minimize damage and prevent recurrence.
Learn more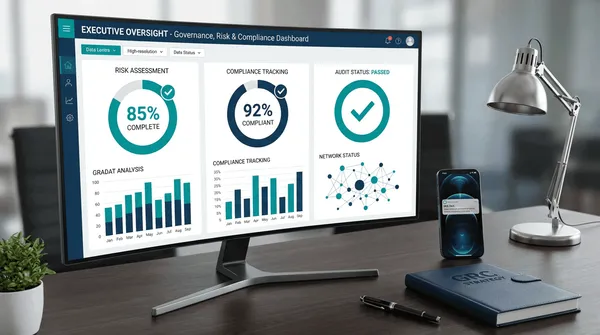
Fully managed IT services for Southern California SMBs. One flat monthly rate covers 24/7 monitoring, patch management, endpoint protection, and vCIO advisory - so your team stays focused on the business, not the infrastructure.
Learn more
End-to-end Microsoft 365 administration, security hardening, license optimization, and independent backup for California businesses. Built for SMBs and mid-market teams that outgrew the default settings.
Learn more
Design, deployment, and management of enterprise network infrastructure including SD-WAN, Wi-Fi, VPN, and multi-site connectivity.
Learn more
24/7 SOC monitoring, SIEM-powered threat detection, and proactive threat hunting to identify and neutralize attacks before they cause damage.
Learn more Targeted IT services covering email and spam protection, data backup and disaster recovery, and Microsoft 365 management for Southern California businesses with specific operational and compliance requirements.
Learn more