POS security and reliable IT for modern retail operations.
Managed IT and security for Southern California retailers protecting POS systems, customer payment data, and PCI-DSS compliance across stores.
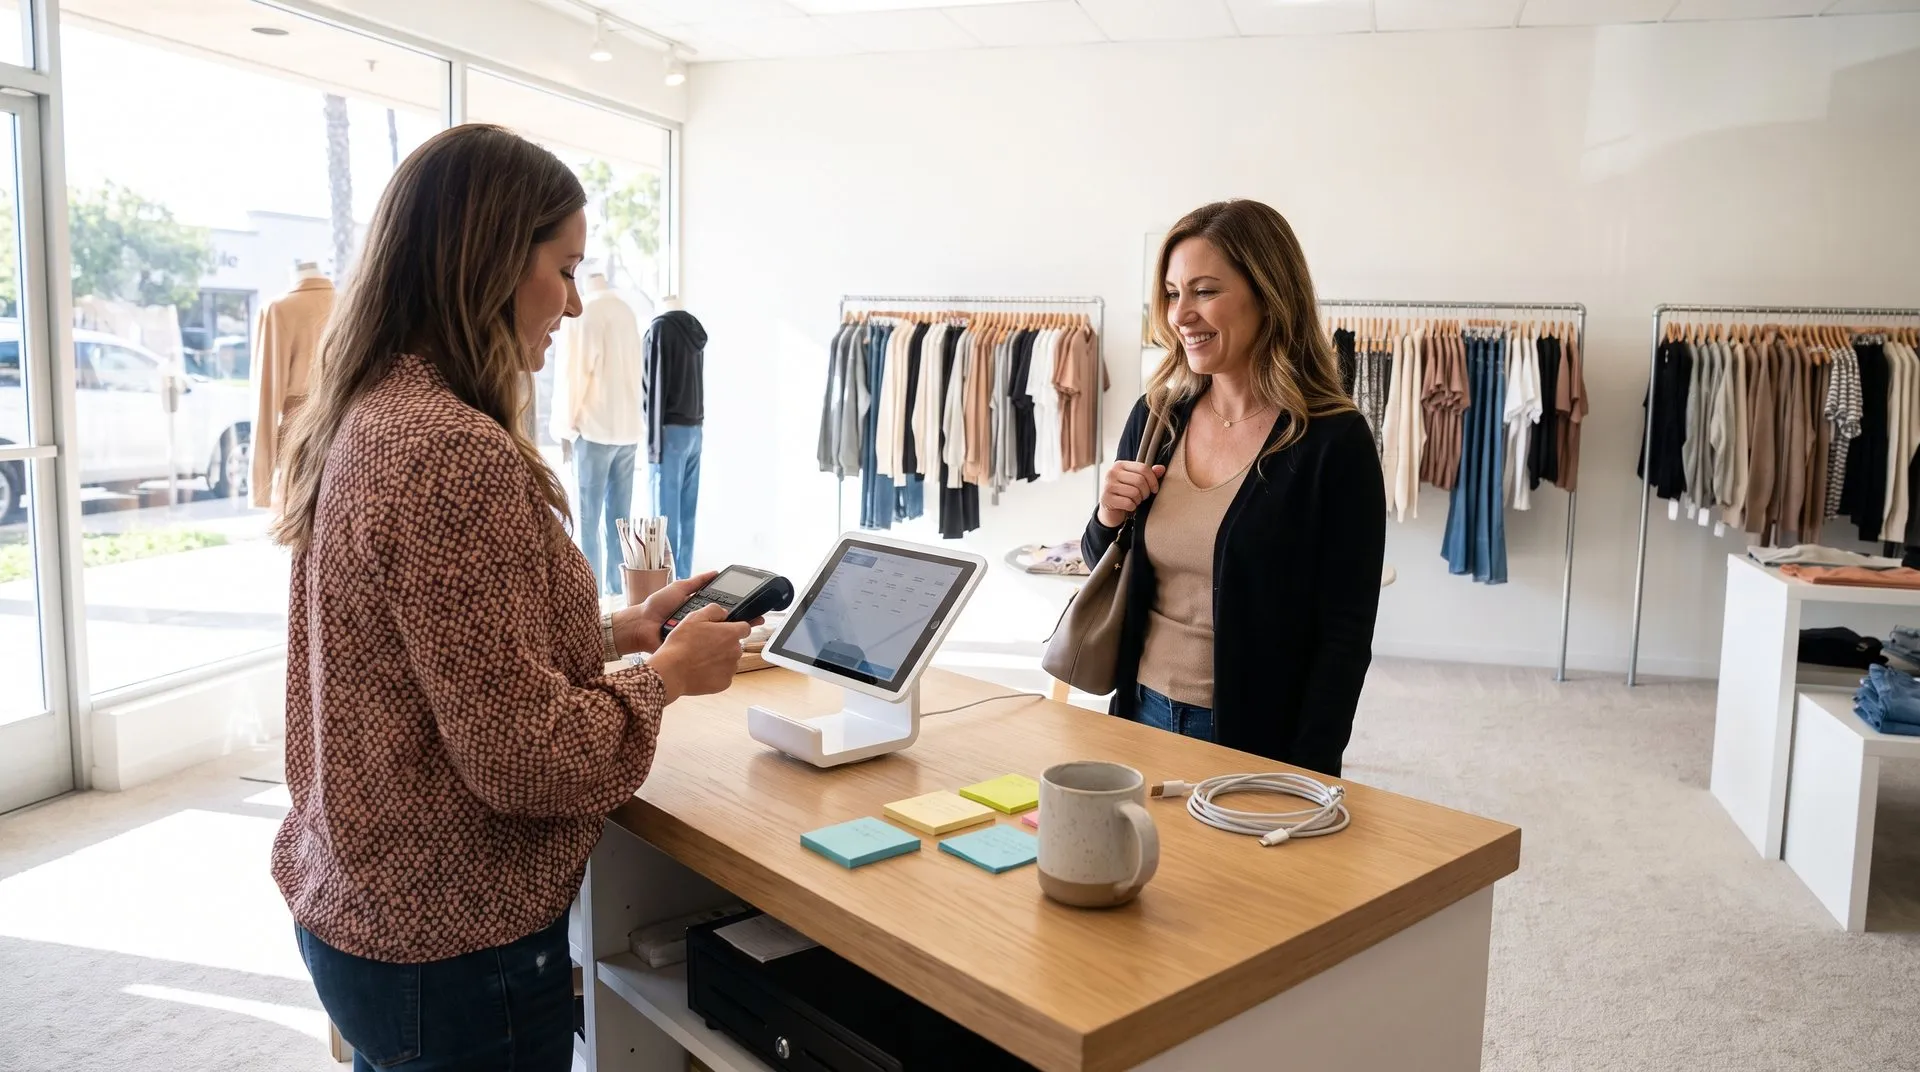
Local response, written into the contract.
Unified IT management and security, tailored for retail.
What we manage
- 01POS system infrastructure management and uptime monitoring
- 02Store and warehouse network administration
- 03E-commerce platform infrastructure support
- 04Inventory and ERP system management
- 05Help desk for store managers and corporate teams
How we protect
- 01PCI-DSS compliance for all payment processing environments
- 02POS malware detection and point-of-sale threat monitoring
- 0324/7 SOC monitoring for store, warehouse, and corporate networks
- 04Guest Wi-Fi network isolation and monitoring
- 05Incident response for payment data breaches
These items remain under your direct control and are out of scope for our managed services.
- In-store customer service and sales operations
- Loss prevention (physical shoplifting)
- Visual merchandising and store design
- Product buying and inventory strategy
Four steps from kickoff to a fully managed environment.
Every engagement starts with an environment assessment: the systems you rely on, the data you handle, the frameworks that govern you, and the gaps to close. The output is a prioritized roadmap with cost and outcomes at 30, 60, and 90 days.
Written environment assessment
A free assessment and gap report of where you stand today, measured against the frameworks your industry answers to. The output is yours to keep whether you engage AdVran or not.
Discovery and documentation
Every device, account, application, and dependency gets catalogued. We document your environment before we manage it, so nothing falls through the cracks.
24/7 monitoring and SOC coverage
Servers, endpoints, firewalls, and cloud workloads are watched around the clock. Alerts fire, and engineers respond, before users notice a problem.
Reports and a written roadmap
A monthly report of every action, change, and risk addressed, plus quarterly reviews that tie technology decisions to business goals and audit deadlines.
Industry analysis & approach.
Every payment terminal in a retail operation is a potential entry point for attackers. And PCI-DSS requires every single one to be in scope. Retailers running multiple locations face a compliance and security problem that scales with every new store, every new register, and every new vendor integration they add.
The IT Challenge
Retail IT looks simple from the outside. It rarely is.
- POS systems are soft targets. Point-of-sale hardware and software often runs on older operating systems with limited patching support. RAM-scraping malware that sits quietly on a terminal and collects card data before encryption is a real, active threat. Not a theoretical one.
- Multi-location sprawl creates gaps. Each store is essentially a remote office with its own network, its own devices, and its own risk surface. Corporate IT teams can't physically be everywhere. Without centralized monitoring, a compromise at one location can go undetected for weeks.
- Guest Wi-Fi is an attack vector. Customers expect free Wi-Fi. But a guest network that's not properly isolated from business systems is an open door. This gets misconfigured constantly (and quietly).
- Vendor and third-party access is hard to control. POS vendors, payment processors, and inventory suppliers all need some level of access. Managing that access. And pulling it when vendor relationships end. Takes process discipline most retail IT teams don't have time for.
AI Is Changing This Industry
AI is reshaping retail through dynamic pricing, inventory prediction, and personalized marketing. And every one of those systems touches customer data. Retail IT teams are getting asked to integrate AI tools they didn't choose, on timelines they didn't set. AdVran helps retail clients evaluate AI platforms for PCI-DSS and data privacy compliance before deployment, so the efficiency gains don't come with a compliance exposure attached.
Compliance
Any retailer processing credit or debit card transactions is in scope for PCI-DSS. And the requirements apply whether payment is handled in-store, online, or through a third-party processor. PCI-DSS v4.0 added new requirements around multi-factor authentication and web skimming prevention that caught a lot of retailers off guard. AdVran manages PCI-DSS compliance programs for retail clients and handles the quarterly vulnerability scanning and annual assessment coordination, so your team isn't reinventing that process every year.
Related Industries
Retail and consumer goods often operate on overlapping supply chains and face similar e-commerce security challenges. Consumer goods companies managing brand data, product catalogs, and digital distribution channels face many of the same PCI-DSS and data privacy obligations as traditional retailers. Companies with travel, logistics, or hospitality operations also share payment data protection requirements. See Travel, Logistics & Hospitality.
Applicable regulatory frameworks.
AdVran ensures your organization meets every requirement for these industry-specific compliance frameworks.
IT services for retail.
Don't see yours? Call (714) 694-4573 or email contact@advran.com.
Managed IT and security for Southern California retailers protecting POS systems, customer payment data, and PCI-DSS compliance across stores.
Key compliance requirements for this industry include PCI-DSS, SOC 2, CCPA/CPRA. AdVran helps you achieve and maintain compliance across all applicable frameworks.
Our Security Operations Center maintains threat intelligence specific to your industry. We track the latest attack patterns, vulnerability disclosures, and compliance changes affecting your sector, and proactively adjust your defenses.
Yes. AdVran integrates with your existing systems and platforms. We perform a thorough assessment of your current environment and build a management plan that builds on your existing investments while addressing gaps.
Other industries we serve.
Defense Contractors
End-to-end IT management and security operations built for the strict compliance and data-protection demands of aerospace and defense contractors.
Explore industry
Construction & Engineering
Managed IT and security for construction firms and engineering companies protecting BIM data, remote job site connectivity, and project files across Southern California.
Explore industry
Financial & Accounting
Managed IT and security operations for banking, capital markets, fintech, and insurance firms operating under PCI-DSS, SOX, and SEC requirements.
Explore industry