Audit-ready compliance maintained continuously, not assembled before an assessment.
Continuous compliance monitoring, audit readiness, and risk management across HIPAA, CMMC, PCI-DSS, SOX, and other regulatory frameworks.
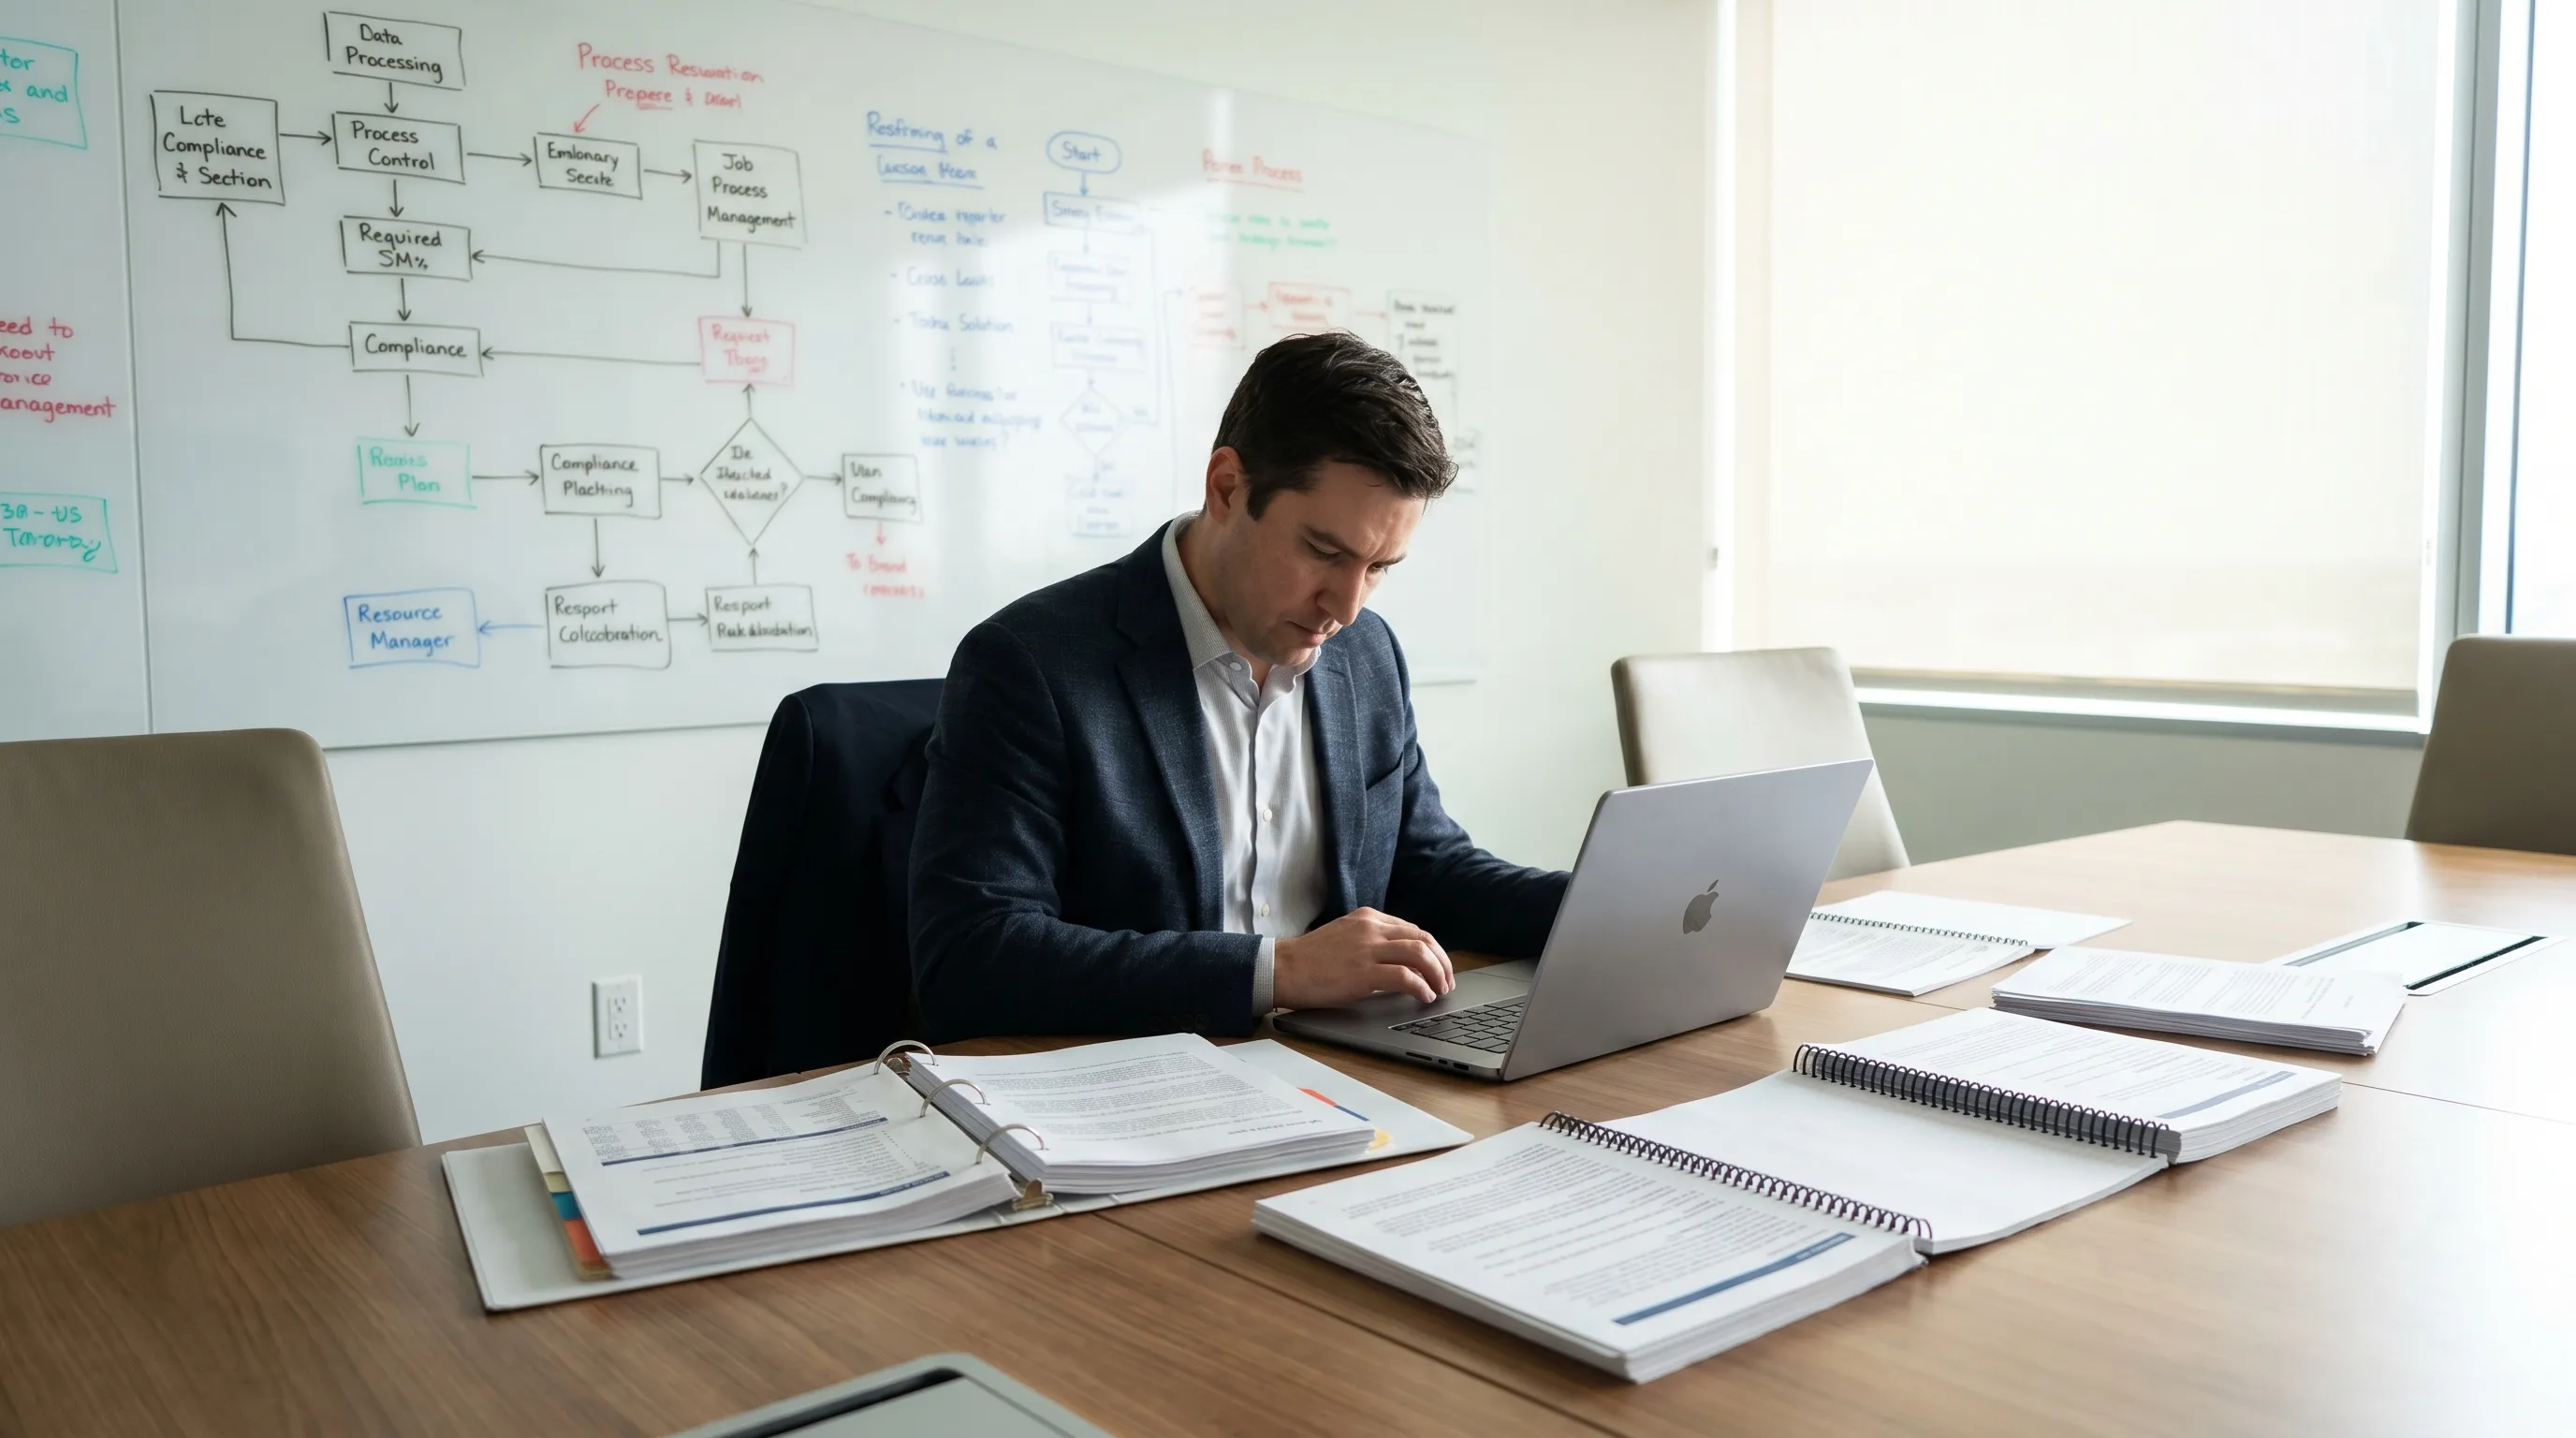
From kickoff to running, step by step.
Every AdVran engagement follows the same documented sequence so nothing slips between handoffs. Most clients reach steady-state operation in four to six weeks.
Framework gap analysis
We baseline your environment against each framework you operate under (HIPAA, CMMC 2.0, SOC 2, PCI-DSS, NIST CSF, and others) and produce a written gap report. No verbal summaries. Written.
Continuous control monitoring
Automated evidence collection runs daily. When a control drifts out of compliance, an alert fires. The audit binder stays current all year, not just the month before an assessment.
Risk register and remediation
Live risk register prioritized by business impact and regulatory exposure. Vulnerabilities tracked through remediation with documented owners and SLAs: no loose ends.
Audit and assessor coordination
When the auditor arrives, evidence packages are organized and control mappings are documented. AdVran coordinates the engagement directly so your team isn't scrambling.
What Is IT Compliance and Risk Management?
IT compliance and risk management is the continuous process of monitoring, documenting, and maintaining your organization's adherence to regulatory frameworks (HIPAA, CMMC, PCI-DSS, SOC 2, NIST) through automated control monitoring, evidence collection, and risk assessment. Organizations with compliance failures experience breaches costing an average of $5.05 million, 22% more than their compliant counterparts, according to IBM's 2024 Cost of a Data Breach Report.
How AdVran Manages Compliance
AdVran maintains your compliance posture in real time, collecting control evidence daily, alerting when controls drift, and keeping documentation organized throughout the year. When an assessment arrives, the evidence package is already assembled, not pulled together under deadline pressure.
What Does Compliance Management Include?
- Multi-framework compliance support across HIPAA, CMMC 2.0, PCI-DSS, SOC 2 readiness, NIST CSF, GLBA, FERPA, DFARS, and other industry frameworks on request, including multi-framework programs for organizations with overlapping requirements
- Continuous control monitoring with automated evidence collection and real-time alerts when controls drift out of compliance
- Risk assessments identifying vulnerabilities and prioritizing remediation by business impact and regulatory exposure
- Vulnerability management with regular scanning, patch tracking, and penetration testing coordination
- Audit preparation including documentation organization, control mapping, findings response, and direct coordination with auditors and assessors
Why Compliance Is a Business-Critical Priority for California Companies
Southern California's industry mix stacks up compliance obligations fast. Healthcare providers in Los Angeles, Anaheim, and San Diego face HIPAA enforcement by HHS OCR. Defense contractors near the aerospace primes in Long Beach, El Segundo, Anaheim, and Pasadena face CMMC requirements that will gate contract bids, not someday but now. Retailers and hospitality companies processing credit cards across the region face PCI-DSS Requirement 6 and 10 mandates. Technology companies serving enterprise customers routinely need SOC 2 Type II reports just to get in the door with large clients.
HHS OCR levied over $6.2 million in HIPAA civil monetary penalties in 2023. Inadequate risk analysis was cited in 71% of those enforcement actions. Not a data breach. Not a ransomware attack. Just inadequate documentation of what the risks were. California's CCPA adds civil penalties up to $7,988 per intentional violation under the 2025 inflation adjustment and creates a private right of action for data breaches, an exposure layer sitting on top of every federal regulatory requirement.
Defense contractors in Southern California may need to demonstrate a CMMC status as a condition of award on covered contracts. The required level and assessment type depend on the solicitation. Our CMMC guide explains Level 2 requirements and the current implementation status.
Who Should Use Managed Compliance Services?
Organizations in regulated industries (healthcare, defense, financial services, retail, education, legal) that need to maintain compliance across one or more frameworks without a dedicated compliance team. Particularly valuable for companies running under multiple frameworks simultaneously, since multi-framework compliance without automation tools typically takes 3-6 weeks just to map control overlaps before remediation work begins.
AdVran was founded by Adrian Monges Rodriguez, a computer engineer with extensive experience managing enterprise IT and network infrastructure for aerospace, defense, and critical infrastructure organizations in Southern California. Documentation, auditability, and disciplined change control weren't optional in those environments. That same standard runs through AdVran's compliance practice: every control is documented, every evidence package is organized, and every audit finding is addressed with the rigor of an engineering discrepancy report.
What Results Can You Expect?
- Always audit-ready with continuously maintained documentation, not assembled under deadline pressure
- Reduced compliance program costs through automated evidence collection and integrated control monitoring
- Clear risk visibility with a live risk register and prioritized remediation roadmap that updates as your environment changes
- Successful audits with fewer findings and faster completion timelines
- Documented compliance posture that satisfies customer due diligence requirements and insurance underwriters
The numbers behind Compliance & Risk Management.
Sources: California Privacy Protection Agency 2025 enforcement actions; CA AG Healthline settlement, July 2025; California SB 446 (effective Jan 1, 2026); IBM Cost of a Data Breach Report 2025
One team manages your IT and secures it.
Most providers either manage your infrastructure or monitor your security. Never both. We do both under one roof, which means when we detect a threat, we remediate it immediately.
Security-first foundation
Every infrastructure decision is filtered through a hardened security lens. Security is a foundational constraint, not an afterthought or an upsell.
Immediate remediation
We don't send you a ticket when something breaks. We fix it directly, because we own the infrastructure you run on.
Two teams, one price
A full Enterprise Operations Center and Security Operations Center, combined into a single, predictable monthly cost.
Proven track record.
Healthcare, defense, finance and education teams trust us with environments where an outage delays patient care and a compliance gap costs a contract.
- Founder's engineering at Boeing, incl. NASA projects
- 4+ yrs
- Endpoints managed
- 3.5k+
- SOC monitoring
- 24/7
“We switched over to AdVran's services after having issues with a previous MSP. Adrian and his team have been incredibly fast in supporting our business operations. If you are looking for an honest and reliable IT partner, I wouldn't look anywhere else.”
Gutierrez ManufacturingManufacturing & OperationsGoogle review 
“The best thing about AdVran is their proactive approach, they anticipate our needs before they become issues. They are incredibly easy to work with and provide quick responses that keep our operations running smoothly.”
Pro Compact Estates LLCReal Estate & DevelopmentGoogle review 
“AdVran has become an invaluable extension of our foundation. They have removed all the IT hurdles we faced before and help guide us forward towards our mission.”
James and Teresa Keller FoundationNon-Profit & PhilanthropyGoogle review “Their support has been dependable from day one. Adrian and his team check in regularly and usually flag issues before we notice them.”
Owner, Brea Electric CompanyElectrical Contracting “The biggest thing that separates AdVran from our last vendor is how much they actually talk to us. Once a month we sit down and they walk us through what's in flight and what's already shipped.”
Founder & Principal, HB FacadeFacade Consulting “The communication was second-to-none. These guys took the time to really understand our business structure and its needs, and made sure we knew what was going on.”
CEO, MQ AwningsAwnings Manufacturing
About Compliance & Risk Management.
Don't see yours? Call (714) 694-4573 or email contact@advran.com.
IT compliance and risk management is the continuous process of documenting, monitoring, and maintaining your organization's adherence to regulatory frameworks like HIPAA, CMMC, PCI-DSS, SOC 2, and NIST CSF. It means identifying gaps in your security controls, collecting evidence that controls are actually working, managing vulnerabilities by business risk, and being able to show an auditor a clean picture at any point during the year, not just when an assessment is coming up.
According to IBM's 2024 Cost of a Data Breach Report, breaches at organizations with compliance failures cost $5.05 million on average, which is 22% more than breaches at compliant organizations. HHS OCR levied over $6.2 million in HIPAA fines in 2023 alone, with 71% of enforcement actions citing inadequate risk analysis. California's CCPA adds civil penalties up to $7,988 per intentional violation under the 2025 inflation adjustment and private right of action for data breaches.
AdVran supports HIPAA (including HITECH), CMMC 2.0 Level 1 and Level 2 readiness under NIST SP 800-171 (including DFARS 252.204-7012), PCI DSS, SOC 2 readiness, NIST CSF, SOX, and CCPA/CPRA, plus the FTC Safeguards Rule (GLBA) for financial and accounting firms and FERPA for schools. We also support other industry frameworks on request. We specialize in multi-framework compliance for organizations that must satisfy several regulatory requirements at once, which is common for California companies in healthcare, defense, and financial services.
Annual audit prep means scrambling in the weeks before an assessment: pulling evidence, finding gaps, doing emergency remediation. Continuous compliance monitoring collects evidence automatically throughout the year, watches controls in real time for failures or drift, and keeps a live posture dashboard current. When an audit arrives, the work is already done. AdVran clients consistently finish audits faster with fewer findings because compliance is maintained daily, not assembled under pressure.
A risk assessment is a structured analysis of your IT environment to find vulnerabilities, evaluate how likely threats are and what they'd cost, and prioritize remediation by business risk. HIPAA requires a regular risk analysis as a foundational compliance requirement. NIST recommends at least annual formal risk assessments with continuous vulnerability monitoring between them. AdVran conducts formal risk assessments aligned to your frameworks and maintains a live risk register that updates as your environment changes.
CMMC requirements apply to covered Department of Defense contracts and subcontracts. Level 2 addresses Controlled Unclassified Information using 110 NIST SP 800-171 Revision 2 requirements. The solicitation specifies whether a self-assessment or a C3PAO assessment is required. AdVran helps Southern California contractors prepare their systems, documentation, and evidence.
Other services we run.
Help Desk & End-User Support
Responsive, security-aware help desk services covering device management, onboarding, offboarding, and day-to-day IT support for your entire workforce.
Explore service
Incident Response & Remediation
Rapid breach containment, forensic investigation, disaster recovery, and post-incident hardening to minimize damage and prevent recurrence.
Explore service
Network Infrastructure Support
Design, deployment, and management of enterprise network infrastructure including SD-WAN, Wi-Fi, VPN, and multi-site connectivity.
Explore service