Cloud Management & Migration
Strategic cloud migration planning and ongoing multi-cloud infrastructure management, ensuring performance, cost optimization, and security at every stage.
Learn moreSan Diego County, CA
San Diego's proximity to Camp Pendleton, Naval Base San Diego, and dozens of DoD facilities makes it one of America's most defense-dependent metro areas, where CMMC certification is rapidly becoming a survival requirement for contractors across the supply chain. AdVran gives San Diego defense, biotech, and government contracting businesses the compliance infrastructure they need to win and keep federal contracts.
Frequently asked questions
Most subcontractors handling Controlled Unclassified Information need CMMC Level 2, which aligns with the 110 controls in NIST SP 800-171. Prime contractors handling higher-sensitivity data may need Level 3. AdVran runs CMMC gap assessments, builds System Security Plans, sets up required controls, and prepares you for C3PAO assessment. We don't perform the actual certification assessment (that's done by accredited third parties), but we get you ready to pass it.
ITAR restricts the export of defense-related technical data, which includes digital transmission to foreign nationals, even employees working in your San Diego office. Companies subject to ITAR need access controls that restrict technical data to U.S. persons, encryption meeting specific standards, and audit trails proving compliance. A single ITAR violation can mean penalties up to $1 million per occurrence and criminal prosecution. AdVran sets up ITAR-compliant information environments including network segmentation, data classification, and access restriction.
Yes. FedRAMP authorization is required for cloud service providers selling to federal agencies. AdVran helps San Diego companies work through the FedRAMP authorization process, set up the required NIST 800-53 controls, prepare documentation packages, and maintain continuous monitoring after authorization. We also support companies that need to use FedRAMP-authorized services and show their own compliance with federal security requirements.
What we offer
Strategic cloud migration planning and ongoing multi-cloud infrastructure management, ensuring performance, cost optimization, and security at every stage.
Learn more
Augment your in-house IT team with AdVran's certified engineers, 24/7 SOC, and compliance experts. Keep the people who know your business; add the depth you cannot hire.
Learn more
Continuous compliance monitoring, audit readiness, and risk management across HIPAA, CMMC, PCI-DSS, SOX, and other regulatory frameworks.
Learn more
Multi-layered cybersecurity for Southern California SMBs: EDR/MDR endpoint protection, email security, identity and access management, vulnerability management, SIEM monitoring, and security awareness training.
Learn more
Immutable backups, tested restore procedures, and disaster recovery as a service for California businesses. Built to actually work when ransomware hits, not just on paper.
Learn more
Responsive, security-aware help desk services covering device management, onboarding, offboarding, and day-to-day IT support for your entire workforce.
Learn more Rapid breach containment, forensic investigation, disaster recovery, and post-incident hardening to minimize damage and prevent recurrence.
Learn more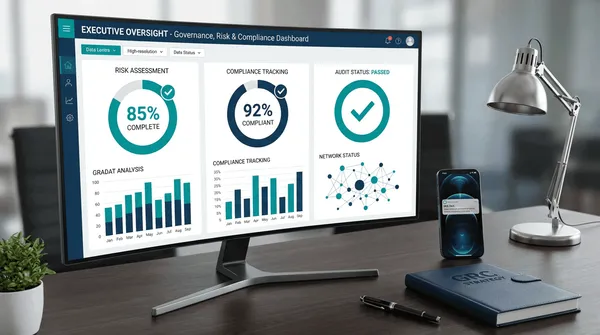
Fully managed IT services for Southern California SMBs. One flat monthly rate covers 24/7 monitoring, patch management, endpoint protection, and vCIO advisory - so your team stays focused on the business, not the infrastructure.
Learn more
End-to-end Microsoft 365 administration, security hardening, license optimization, and independent backup for California businesses. Built for SMBs and mid-market teams that outgrew the default settings.
Learn more
Design, deployment, and management of enterprise network infrastructure including SD-WAN, Wi-Fi, VPN, and multi-site connectivity.
Learn more
24/7 SOC monitoring, SIEM-powered threat detection, and proactive threat hunting to identify and neutralize attacks before they cause damage.
Learn more Targeted IT services covering email and spam protection, data backup and disaster recovery, and Microsoft 365 management for Southern California businesses with specific operational and compliance requirements.
Learn more