Cloud Management & Migration
Strategic cloud migration planning and ongoing multi-cloud infrastructure management, ensuring performance, cost optimization, and security at every stage.
Learn moreOrange County, CA
Anaheim processes more payment card transactions per square mile than almost any city in California, driven by Disneyland Resort, the Convention Center, and the surrounding hospitality corridor. That volume makes PCI-DSS compliance a defining operational requirement here, not an abstract IT concern. AdVran builds compliance programs matched to Anaheim's transaction-heavy hospitality sector, its corporate headquarters, and its precision manufacturing base.
Frequently asked questions
Any business that accepts, processes, stores, or transmits payment card data must comply with PCI-DSS. For Anaheim's hospitality businesses, that means hotels processing thousands of daily transactions, restaurants with point-of-sale terminals, and convention centers handling event payments. You're looking at secure networks, protected cardholder data, vulnerability management, access controls, and documented security policies. Your specific PCI level depends on transaction volume. AdVran helps Anaheim hospitality businesses figure out where they land and set up the controls to back it up.
Publicly traded companies headquartered in Anaheim, particularly in the Platinum Triangle and Anaheim Hills business districts, must satisfy SOX Section 404 requirements for internal controls over financial reporting. That covers IT general controls around access management, change management, system operations, and data backup for financial systems. AdVran sets up the IT controls framework that SOX auditors test, so your financial reporting infrastructure actually meets Section 404 requirements when the auditors show up.
Aerospace and defense manufacturers in Anaheim typically need AS9100 certification and may face ITAR, DFARS, or CMMC requirements depending on their customer base. Medical device manufacturers need FDA 21 CFR Part 820 quality system regulation compliance. Both sectors increasingly require digital quality records with integrity controls, validated systems, and electronic signature compliance under 21 CFR Part 11 where applicable. AdVran gives you the IT infrastructure and security controls that hold these quality management systems together.
What we offer
Strategic cloud migration planning and ongoing multi-cloud infrastructure management, ensuring performance, cost optimization, and security at every stage.
Learn more
Augment your in-house IT team with AdVran's certified engineers, 24/7 SOC, and compliance experts. Keep the people who know your business; add the depth you cannot hire.
Learn more
Continuous compliance monitoring, audit readiness, and risk management across HIPAA, CMMC, PCI-DSS, SOX, and other regulatory frameworks.
Learn more
Multi-layered cybersecurity for Southern California SMBs: EDR/MDR endpoint protection, email security, identity and access management, vulnerability management, SIEM monitoring, and security awareness training.
Learn more
Immutable backups, tested restore procedures, and disaster recovery as a service for California businesses. Built to actually work when ransomware hits, not just on paper.
Learn more
Responsive, security-aware help desk services covering device management, onboarding, offboarding, and day-to-day IT support for your entire workforce.
Learn more Rapid breach containment, forensic investigation, disaster recovery, and post-incident hardening to minimize damage and prevent recurrence.
Learn more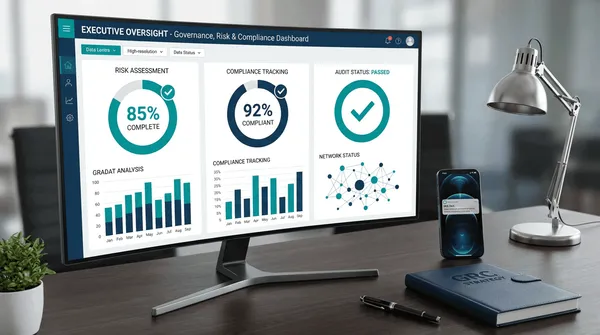
Fully managed IT services for Southern California SMBs. One flat monthly rate covers 24/7 monitoring, patch management, endpoint protection, and vCIO advisory - so your team stays focused on the business, not the infrastructure.
Learn more
End-to-end Microsoft 365 administration, security hardening, license optimization, and independent backup for California businesses. Built for SMBs and mid-market teams that outgrew the default settings.
Learn more
Design, deployment, and management of enterprise network infrastructure including SD-WAN, Wi-Fi, VPN, and multi-site connectivity.
Learn more
24/7 SOC monitoring, SIEM-powered threat detection, and proactive threat hunting to identify and neutralize attacks before they cause damage.
Learn more Targeted IT services covering email and spam protection, data backup and disaster recovery, and Microsoft 365 management for Southern California businesses with specific operational and compliance requirements.
Learn more